Understanding Audit And Compliance
Introduction
Audit and compliance are fundamental disciplines that promote accountability, transparency, integrity, and continual improvement. They provide structured mechanisms for evaluating activities, verifying conformity with established requirements, assessing the effectiveness of controls, and providing confidence that responsibilities are performed consistently and objectively.
The principles of audit and compliance are universal and apply across commercial enterprises, government agencies, critical infrastructure, healthcare, financial services, manufacturing, education, non-profit organizations, and many other sectors. While legal obligations, operational environments, and business objectives may vary, the underlying concepts, principles, and objectives of audit and compliance remain consistent.
Today’s environment is governed by an increasing number of legal, regulatory, contractual, industry, and internal requirements. At the same time, rapid technological advancement, digital transformation, interconnected systems, globalization, and evolving risks have significantly increased operational complexity. Simply establishing policies, procedures, and controls is no longer sufficient. Their implementation must be monitored, their effectiveness verified, and their suitability continually evaluated to ensure they remain capable of achieving their intended objectives.
Audit and compliance provide the structured disciplines needed to achieve these outcomes. Together, they help ensure that established requirements are consistently fulfilled, controls operate effectively, responsibilities are appropriately discharged, and opportunities for improvement are identified before they develop into significant issues.
Although closely related, audit and compliance are distinct disciplines with different responsibilities. Compliance focuses on achieving and maintaining conformity with applicable requirements, while audit provides independent assurance that those requirements, processes, and controls are effective. Together, they contribute to accountability, operational excellence, continual improvement, and stakeholder confidence.
This article introduces the fundamental concepts, principles, objectives, and practices of audit and compliance and explains how these disciplines work together to support effective governance, risk management, internal controls, and organizational performance across all sectors.
What is Audit?
An audit is a systematic, independent, objective, and documented examination of activities, processes, systems, records, controls, or operations to determine whether they conform to established criteria and whether those criteria are being achieved effectively.
The primary purpose of an audit is to provide independent assurance based on objective evidence. Rather than assuming that activities are being performed correctly or that controls are operating effectively, an audit evaluates evidence to determine whether established requirements are being satisfied and whether opportunities exist to improve efficiency, effectiveness, and performance.
Audits are performed against predefined criteria, which may include laws, regulations, standards, contractual obligations, organizational policies, procedures, management system requirements, or other recognized benchmarks.
Depending on its objectives, an audit may evaluate governance, finance, operations, information technology, cybersecurity, physical security, quality management, environmental management, health and safety, business continuity, supply chain management, or any other functional area.
Auditors collect evidence through documentation reviews, interviews, observations, inspections, sampling, technical testing, and analytical procedures. Their conclusions are based on factual, verifiable evidence rather than assumptions or personal opinions.
One of the defining characteristics of auditing is independence. Auditors perform their work objectively and impartially, enabling governing bodies, management, regulators, and other stakeholders to rely on the credibility of audit findings and recommendations.
Modern auditing extends beyond identifying deficiencies. It also evaluates the effectiveness of management systems, internal controls, governance processes, and operational practices while supporting continual improvement and organizational resilience.
Objectives of Audit
The primary objectives of an audit are to:
- Verify conformity with established requirements.
- Evaluate the effectiveness of controls.
- Assess the efficiency and effectiveness of processes.
- Identify non-conformities, weaknesses, and improvement opportunities.
- Provide independent and objective assurance.
- Support informed decision-making.
- Recommend corrective and preventive improvements.
- Promote continual improvement.
Characteristics of Audit
An effective audit is:
- Independent
- Objective
- Systematic
- Evidence-based
- Documented
- Transparent
- Repeatable
- Improvement-oriented
Benefits of Audit
Effective auditing helps to:
- Improve accountability and transparency.
- Strengthen internal controls.
- Enhance operational effectiveness.
- Identify process weaknesses.
- Support legal and regulatory obligations.
- Improve stakeholder confidence.
- Reduce organizational risk.
- Promote continual improvement.
What is Compliance?
Compliance is the continual process of ensuring that activities, processes, systems, products, services, and operations conform to applicable legal, regulatory, contractual, industry, and internal requirements.
Compliance involves establishing policies, procedures, controls, monitoring activities, reporting mechanisms, and supporting evidence necessary to demonstrate ongoing conformity with applicable obligations. It is not a one-time activity but a continuous discipline that adapts to changes in legislation, regulations, standards, technologies, organizational objectives, and stakeholder expectations.
Compliance requirements originate from numerous sources, including legislation, regulations, regulatory authorities, contractual agreements, industry standards, organizational policies, governance frameworks, and professional codes of conduct.
Maintaining compliance requires continuous monitoring, periodic assessments, documentation, employee awareness, corrective actions, and management oversight to ensure that applicable requirements continue to be satisfied.
An effective compliance function promotes lawful operations, ethical conduct, operational consistency, accountability, and stakeholder confidence while minimizing legal, regulatory, financial, operational, and reputational risks.
Objectives of Compliance
Compliance aims to:
- Meet legal and regulatory obligations.
- Fulfil contractual commitments.
- Adhere to applicable standards and frameworks.
- Enforce organizational policies and procedures.
- Promote ethical conduct.
- Reduce compliance-related risks.
- Maintain continual conformity.
- Build stakeholder confidence.
Sources of Compliance Requirements
Compliance requirements commonly originate from:
- Laws
- Regulations
- Regulatory authorities
- Industry standards
- Contractual obligations
- Customer requirements
- Internal policies
- Governance frameworks
- Professional codes of conduct
Benefits of Compliance
Effective compliance helps to:
- Reduce legal and regulatory exposure.
- Improve operational consistency.
- Demonstrate accountability.
- Strengthen stakeholder confidence.
- Protect reputation.
- Support sustainable operations.
- Promote ethical conduct.
- Enable continual improvement.
Relationship Between Audit and Compliance
Audit and compliance are complementary disciplines that work together to ensure that established requirements are consistently implemented, maintained, evaluated, and improved. Although they perform different functions, they share a common objective of promoting accountability, transparency, conformity, and continual improvement.
Compliance establishes the policies, procedures, controls, and monitoring activities necessary to achieve and maintain conformity with applicable legal, regulatory, contractual, industry, and internal requirements. It focuses on integrating these requirements into everyday activities and maintaining evidence that demonstrates ongoing adherence.
Audit provides an independent and objective assessment of these activities. It evaluates whether compliance processes, internal controls, and supporting evidence are appropriately designed, effectively implemented, and operating as intended. Through evidence-based assessments, audit identifies strengths, weaknesses, non-conformities, and opportunities for improvement.
The relationship between audit and compliance is therefore collaborative rather than independent. Compliance establishes and maintains conformity, while audit independently verifies its effectiveness. Findings from audits often result in corrective actions that strengthen compliance programs, while mature compliance processes provide auditors with documented evidence, established controls, and measurable activities that support effective assurance.
Neither discipline replaces the other. Compliance without independent auditing may fail to identify ineffective controls or hidden weaknesses, while auditing alone cannot achieve compliance if applicable requirements are not properly implemented and maintained. Together, audit and compliance create a continuous cycle of implementation, evaluation, improvement, and assurance that supports governance, effective risk management, operational excellence, and stakeholder confidence.
How Audit and Compliance Work Together
- Compliance establishes and maintains conformity with applicable requirements.
- Audit independently evaluates the effectiveness of compliance activities and controls.
- Compliance continuously monitors adherence to obligations.
- Audit verifies whether compliance activities achieve their intended objectives.
- Compliance implements corrective actions to address identified issues.
- Audit validates the effectiveness of corrective actions.
- Compliance supports operational accountability.
- Audit provides independent assurance to governing bodies and stakeholders.
- Together, audit and compliance strengthen governance, support effective risk management, and promote continual improvement.
Why Audit and Compliance Matter
Every activity, whether operational, financial, technological, administrative, or security-related, is expected to achieve defined objectives while complying with applicable requirements. However, without mechanisms to verify performance and conformity, it becomes difficult to determine whether activities are functioning as intended or whether emerging issues remain undetected.
Audit and compliance provide these verification mechanisms. They establish confidence that requirements are understood, responsibilities are fulfilled, controls operate effectively, and deviations are identified and addressed in a timely manner. Together, they enable informed decision-making based on objective evidence rather than assumptions.
The importance of audit and compliance extends beyond regulatory obligations. They support effective management by improving visibility into operations, identifying weaknesses, reducing uncertainty, and encouraging continual improvement. Whether applied to finance, information technology, quality management, environmental management, health and safety, cybersecurity, or any other discipline, these functions help ensure consistency, accountability, and reliability.
Without effective audit and compliance practices, entities may experience:
- Undetected control failures
- Regulatory or legal violations
- Financial losses
- Operational inefficiencies
- Increased risk exposure
- Poor decision-making due to inaccurate or incomplete information
- Loss of stakeholder confidence
- Reputational damage
By identifying deficiencies before they become significant problems, audit and compliance contribute to long-term resilience and sustainable operations.
Building Trust and Accountability
Trust is established when activities are performed consistently, transparently, and in accordance with defined requirements. Audit and compliance provide objective evidence that responsibilities are being fulfilled and that decisions are supported by appropriate controls and documentation.
This accountability extends to governing bodies, executive management, regulators, customers, business partners, employees, shareholders, and the public. Independent assurance and demonstrated conformity increase confidence that resources are managed responsibly and objectives are being achieved.
Supporting Effective Decision-Making
Reliable decisions require reliable information.
Audit provides factual observations regarding the effectiveness of processes, controls, and management systems, while compliance demonstrates whether obligations are being met consistently. Together, they provide management with credible information for prioritizing improvements, allocating resources, managing risks, and planning future activities.
Rather than relying solely on assumptions or periodic reviews, decision-makers gain objective insight into current performance and areas requiring attention.
Improving Operational Performance
Well-designed audit and compliance activities often reveal opportunities to improve efficiency, consistency, and effectiveness.
Examples include:
- Eliminating redundant processes
- Standardizing procedures
- Improving documentation
- Strengthening internal controls
- Clarifying roles and responsibilities
- Enhancing communication between functions
- Reducing recurring non-conformities
Continual evaluation encourages entities to evolve their practices rather than simply maintaining existing processes.
Supporting Legal and Regulatory Obligations
Many industries operate under legal and regulatory requirements that specify minimum expectations for governance, operations, reporting, safety, security, privacy, environmental protection, financial management, and quality.
Compliance helps integrate these obligations into everyday activities, while audit independently evaluates whether they have been implemented effectively.
Demonstrating both conformity and independent assurance helps reduce regulatory exposure and supports regulatory inspections, certifications, and external assessments.
Strengthening Internal Controls
Internal controls are implemented to safeguard assets, improve reliability, reduce risk, prevent errors, and support operational objectives.
Audit evaluates whether these controls are appropriately designed and operating effectively. Compliance helps ensure that required controls are consistently implemented and maintained.
Together, they contribute to stronger control environments and greater confidence in operational activities.
Enabling Continual Improvement
No management system, operational process, or control environment remains perfect indefinitely.
Changes in technology, legislation, stakeholder expectations, operational practices, and emerging risks require periodic evaluation and improvement.
Audit identifies opportunities for enhancement through independent assessment, while compliance ensures improvements are incorporated into operational practices and continue to meet applicable requirements.
This creates an ongoing cycle of evaluation, improvement, implementation, and verification.
Objectives of Audit and Compliance
Although audit and compliance perform different functions, they ultimately support many of the same objectives. Their combined purpose extends beyond satisfying external requirements to improving performance, strengthening accountability, and providing confidence that activities achieve their intended outcomes.
Verify Conformity
Determine whether activities, processes, systems, and controls conform to applicable legal, regulatory, contractual, industry, and internal requirements.
Provide Independent Assurance
Provide objective evidence that activities are operating as intended and that controls remain effective in achieving their objectives.
Evaluate Internal Controls
Assess the design, implementation, operation, and effectiveness of preventive, detective, corrective, compensating, and recovery controls.
Support Effective Governance
Provide governing bodies and management with reliable information that supports oversight, accountability, and informed decision-making.
Strengthen Risk Management
Evaluate whether identified risks are appropriately managed and whether implemented controls adequately address those risks.
Identify Non-Conformities
Detect deviations from established requirements, policies, standards, or procedures before they develop into larger operational, legal, financial, or security issues.
Promote Accountability
Clearly establish responsibilities for implementing requirements, maintaining controls, documenting activities, and addressing identified deficiencies.
Improve Operational Effectiveness
Identify opportunities to streamline activities, improve consistency, eliminate inefficiencies, and enhance overall performance.
Support Continual Improvement
Provide recommendations and evidence that enable processes, controls, and management systems to evolve and improve over time.
Enhance Stakeholder Confidence
Demonstrate to governing bodies, regulators, customers, business partners, investors, employees, and other stakeholders that activities are managed responsibly and in accordance with established requirements.
Create Measurable Value
Modern audit and compliance are not limited to identifying problems. They contribute measurable value by improving performance, reducing uncertainty, strengthening controls, supporting strategic objectives, and enabling sustainable growth.
When implemented effectively, audit and compliance become strategic enablers that help entities achieve operational excellence while maintaining accountability, integrity, and trust.
Role of Audit and Compliance in Security Governance
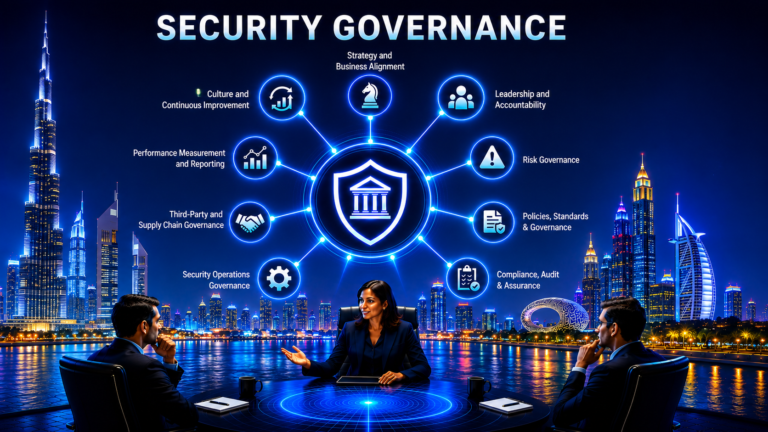
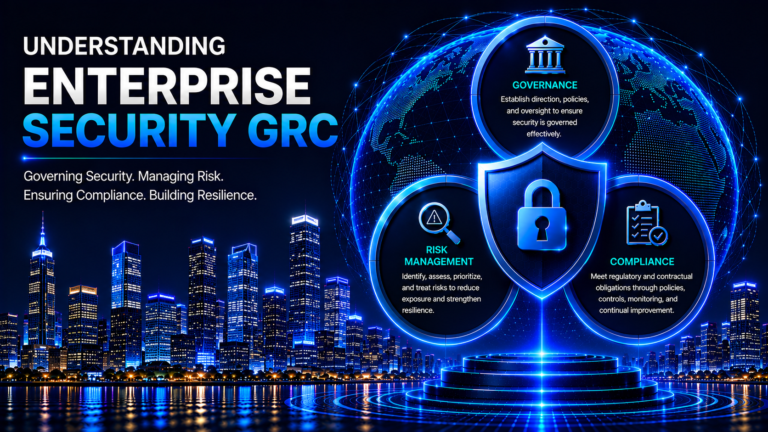
Security Governance establishes the direction, authority, accountability, and oversight necessary to protect an organization’s information, technology, people, physical assets, and business operations. It provides the framework through which security objectives are aligned with organizational goals, security policies are established, responsibilities are assigned, and security performance is monitored.
Audit and compliance are integral components of Security Governance because they help determine whether governance decisions are implemented effectively and achieve their intended objectives. While governance defines what should be achieved, compliance helps ensure that established requirements are followed, and audit independently evaluates whether the relevant processes and controls are functioning as intended.
Compliance translates governance decisions into operational requirements through policies, standards, procedures, and controls. It helps ensure that applicable legal, regulatory, contractual, and internal requirements are integrated into organizational activities.
Audit provides independent and objective assessments of governance processes, control effectiveness, policy implementation, and organizational performance against established criteria. These assessments help determine whether responsibilities are fulfilled, requirements are met, and governance objectives are being achieved.
Without effective audit and compliance, governing bodies and management may have limited visibility into whether governance arrangements are functioning as intended. Together, audit and compliance support transparency, accountability, informed decision-making, and continual improvement.
Supporting Governance Oversight
Governance requires accurate and objective information to support effective oversight and decision-making.
Audit provides independent assessments of governance processes, internal controls, policy implementation, and overall governance effectiveness. Compliance provides information and evidence about adherence to applicable requirements across the organization.
Together, they help governing bodies and management evaluate performance, identify weaknesses, and determine whether corrective actions are necessary.
Verifying Policy Implementation
Security policies establish expectations for protecting information and other organizational assets.
Compliance supports the implementation of these policies through standards, procedures, and operational practices. Audit independently evaluates whether policy requirements have been implemented consistently and whether the associated controls and processes are operating effectively.
This verification helps identify implementation gaps before they develop into significant governance issues.
Strengthening Accountability
Effective governance depends on clearly defined responsibilities and accountability.
Compliance helps establish and maintain responsibilities for meeting applicable requirements. Audit evaluates whether responsibilities are appropriately assigned, understood, and fulfilled.
Together, they strengthen accountability across governing bodies, management, and operational functions.
Supporting Strategic Decision-Making
Security Governance requires decisions concerning priorities, investments, resource allocation, performance, and security improvements.
Audit findings and compliance reporting provide objective information that supports planning and informed decision-making. Decision-makers can use assessment results, documented findings, and compliance information to prioritize improvements.
Promoting Continual Governance Improvement
Security Governance must adapt to changes in organizational objectives, operations, technologies, threats, regulations, and stakeholder expectations.
Audit identifies weaknesses, evaluates the effectiveness of existing arrangements, and recommends improvements. Compliance helps ensure that approved requirements and corrective measures are incorporated into organizational practices and maintained.
Together, they support the continued effectiveness and maturity of Security Governance.
Key Contributions of Audit and Compliance to Security Governance
Audit and compliance support Security Governance by:
- Verifying the implementation of security policies and established requirements.
- Providing independent assurance to governing bodies and management.
- Monitoring conformity with legal, regulatory, contractual, and internal obligations.
- Evaluating the effectiveness of governance processes and security controls.
- Identifying weaknesses, non-conformities, and improvement opportunities.
- Strengthening accountability across organizational functions.
- Supporting evidence-based decision-making.
- Promoting transparency and continual improvement.
Role of Audit and Compliance in Cyber Risk Management
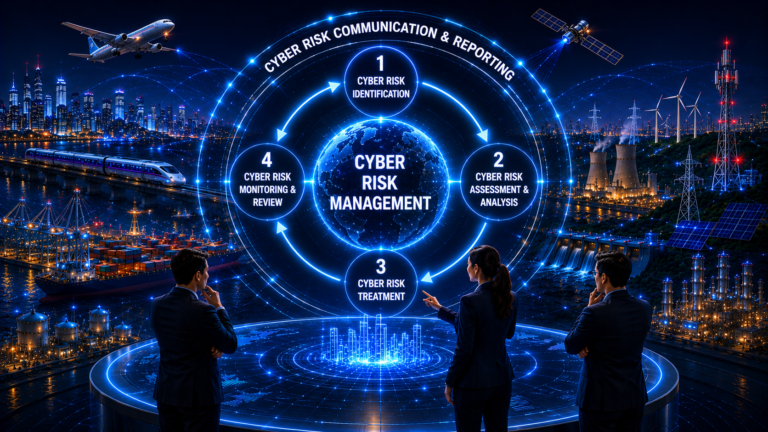
Cyber Risk Management is a structured approach to identifying, assessing, evaluating, treating, monitoring, and communicating risks that may affect information, technology, people, physical assets, business operations, and organizational objectives.
Audit and compliance play complementary roles in Cyber Risk Management by providing assurance that cybersecurity risks are appropriately managed and that risk treatment activities remain effective over time.
Compliance helps ensure that cyber risk management activities align with applicable legal, regulatory, contractual, industry, and organizational requirements. It integrates risk-related obligations into policies, standards, procedures, and operational controls while monitoring conformity with those requirements.
Audit independently evaluates the effectiveness of the Cyber Risk Management framework. Through evidence-based assessments, auditors determine whether risks have been appropriately identified, assessed, treated, monitored, and communicated, and whether implemented controls effectively reduce risks to acceptable levels.
Together, audit and compliance help ensure that cyber risk management remains structured, measurable, and aligned with organizational objectives.
Verifying Risk Management Processes
Risk management processes should be consistently applied across relevant organizational functions and operational areas.
Audit evaluates whether risk identification, assessment, treatment, monitoring, and reporting processes are operating as intended. Compliance helps ensure these processes satisfy applicable requirements and established organizational practices.
Evaluating Risk Controls
Risk treatment depends on the effective implementation of controls.
Audit evaluates whether preventive, detective, corrective, compensating, and recovery controls adequately address identified cyber risks. Compliance monitors whether these controls continue to satisfy applicable requirements.
Together, they improve confidence in the effectiveness of risk treatment activities.
Supporting Risk-Based Decision-Making
Effective risk management requires reliable information.
Audit provides objective assessments of the effectiveness of controls and risk management activities. Compliance supplies evidence demonstrating ongoing conformity with risk-related obligations.
This information enables management to make informed decisions regarding risk priorities, resource allocation, and future improvements.
Monitoring Residual Risk
Not every cyber risk can be completely eliminated.
Following the implementation of risk treatment measures, some level of residual risk usually remains. Audit evaluates whether risk assessment and treatment processes appropriately address residual risks against established criteria. Compliance helps ensure that applicable obligations and monitoring requirements continue to be met.
Risk acceptance decisions remain with the designated risk owners and authorized decision-makers, in accordance with the organization’s governance arrangements.
Driving Continual Improvement
Risk management frameworks require regular review to remain effective.
Audit identifies weaknesses, emerging issues, and improvement opportunities within the Cyber Risk Management framework. Compliance supports the implementation of corrective actions and helps ensure that improvements continue to satisfy applicable requirements.
Together, they strengthen the maturity and effectiveness of cyber risk management.
Types of Audits
Audits are conducted for different purposes depending on the objectives, scope, regulatory requirements, industry, and operational needs of an entity. While all audits follow the same fundamental principles of independence, objectivity, and evidence-based evaluation, they differ in what they examine and the outcomes they seek to achieve.
Understanding the various types of audits helps determine the appropriate approach for evaluating governance, management systems, operational activities, financial processes, information systems, security controls, regulatory obligations, and organizational performance.
Internal Audit
An internal audit is conducted by an organization’s internal audit function or by authorized personnel acting on its behalf. Its primary purpose is to provide independent assurance to management and governing bodies regarding the effectiveness of governance, risk management, internal controls, and operational processes.
Internal audits evaluate whether established policies, procedures, and controls are functioning as intended while identifying opportunities for improvement.
Typical objectives include:
- Evaluating internal controls.
- Assessing operational effectiveness.
- Verifying policy implementation.
- Supporting governance oversight.
- Recommending process improvements.
External Audit
An external audit is performed by an independent party outside the entity being audited. Depending on its purpose and relationship with the audited entity, an external audit may be classified as either a second-party audit or a third-party audit. External audits provide objective assurance to customers, regulators, certification bodies, investors, governing bodies, and other interested parties.
First-Party Audit
A first-party audit is conducted by, or on behalf of, the entity itself to evaluate its own activities, processes, or management systems. It is commonly referred to as an internal audit and is primarily performed to assess conformity with internal requirements, identify improvement opportunities, and prepare for external assessments.
Examples include:
- Internal management system audits.
- Departmental audits.
- Process audits.
- Operational audits.
- Readiness assessments before certification.
Second-Party Audit
A second-party audit is conducted by an organization that has a direct business relationship with the entity being audited. It is typically performed by customers, clients, contractors, or organizations acting on their behalf to verify that suppliers or service providers satisfy contractual and business requirements.
Examples include:
- Customer audits of suppliers.
- Supplier qualification audits.
- Contractor assessments.
- Vendor security assessments.
- Supply chain audits.
Second-party audits help strengthen supplier relationships, improve quality, and reduce supply chain risks.
Third-Party Audit
A third-party audit is conducted by an independent organization that has no direct commercial interest or operational responsibility for the entity being audited. Its purpose is to provide impartial and objective assurance regarding conformity with established requirements, standards, regulations, or contractual obligations. Because third-party auditors are independent of both the auditee and its customers, their findings are generally regarded as highly credible and objective.
Third-party audits are commonly performed to assess conformity with management system standards, regulatory requirements, industry frameworks, financial reporting requirements, or certification programs. Depending on the scope, they may evaluate governance, operational processes, internal controls, management systems, security practices, regulatory compliance, or financial records.
Examples include:
- Certification audits conducted by accredited certification bodies.
- Regulatory inspections performed by government or regulatory authorities.
- Independent financial statement audits.
- External compliance assessments.
- Accreditation assessments.
- Independent security assessments.
Financial Audit
A financial audit evaluates financial records, transactions, statements, and reporting processes to determine whether financial information is complete, accurate, and prepared according to applicable accounting standards and legal requirements.
Financial audits help improve confidence among shareholders, investors, regulators, lenders, and governing bodies.
Operational Audit
An operational audit examines business processes, operational activities, and resource utilization to determine whether operations are efficient, effective, and aligned with organizational objectives.
Operational audits often focus on:
- Process efficiency.
- Resource utilization.
- Performance measurement.
- Operational controls.
- Continuous improvement.
Compliance Audit
A compliance audit evaluates whether activities conform to applicable legal, regulatory, contractual, industry, and internal requirements.
Compliance audits commonly assess:
- Laws and regulations.
- Organizational policies.
- Industry standards.
- Contractual obligations.
- Internal procedures.
Their objective is to identify non-conformities and ensure ongoing compliance.
Information Technology (IT) Audit
An Information Technology audit evaluates the governance, management, operation, and security of information technology resources.
Typical audit areas include:
- IT governance.
- Infrastructure.
- Applications.
- Networks.
- Data management.
- System availability.
- Change management.
- IT operations.
IT audits help ensure that technology supports business objectives while maintaining reliability, integrity, and availability.
Cybersecurity Audit
A cybersecurity audit evaluates cybersecurity governance, security controls, policies, procedures, technologies, and operational practices designed to protect information systems and digital assets.
Common areas include:
- Identity and access management.
- Network security.
- Endpoint security.
- Security monitoring.
- Incident response.
- Data protection.
- Vulnerability management.
- Security awareness.
Cybersecurity audits assess whether security controls effectively reduce cyber risks.
Management System Audit
Management system audits evaluate whether management systems conform to established standards and organizational requirements.
Examples include:
- Information Security Management Systems (ISMS)
- Quality Management Systems (QMS)
- Environmental Management Systems (EMS)
- Business Continuity Management Systems (BCMS)
These audits determine whether management systems are effectively implemented and continually improved.
Types of Compliance
Compliance requirements originate from various sources and apply across different industries, sectors, and operational environments. Most entities are required to comply with multiple obligations simultaneously, including legal requirements, regulatory mandates, contractual commitments, industry standards, and internal governance requirements.
Understanding the different types of compliance helps establish effective compliance programs, implement appropriate controls, allocate responsibilities, and maintain continual conformity with applicable obligations.
Legal Compliance
Legal compliance refers to adherence to laws enacted by national, regional, or local governments. Every entity must comply with the legislation applicable to the jurisdictions in which it operates.
Examples include:
- Labour and employment laws.
- Consumer protection laws.
- Privacy and data protection laws.
- Environmental laws.
- Tax laws.
- Intellectual property laws.
- Competition and antitrust laws.
Failure to comply with legal requirements may result in legal proceedings, financial penalties, civil liabilities, or criminal prosecution.
Regulatory Compliance
Regulatory compliance involves adhering to rules, regulations, directives, and guidelines established by regulatory authorities responsible for overseeing specific industries or activities.
Unlike legislation, regulations are issued by regulatory agencies to implement and enforce legal requirements within their respective sectors.
Examples include:
- Banking and financial regulations.
- Healthcare regulations.
- Telecommunications regulations.
- Aviation regulations.
- Energy and utilities regulations.
- Pharmaceutical regulations.
Regulatory compliance often requires continuous monitoring, periodic reporting, inspections, and independent assessments.
Contractual Compliance
Contractual compliance ensures that obligations agreed upon through contracts, agreements, and service arrangements are fulfilled throughout the duration of the relationship.
Contractual obligations frequently include operational, technical, security, privacy, quality, and performance requirements.
Examples include:
- Service Level Agreements (SLAs).
- Customer contracts.
- Supplier agreements.
- Outsourcing agreements.
- Data processing agreements.
- Confidentiality agreements.
- Licensing agreements.
Maintaining contractual compliance strengthens business relationships and reduces legal and commercial disputes.
Standards Compliance
Standards compliance refers to conformity with nationally or internationally recognized standards developed by standards organizations, professional bodies, or industry groups.
Standards provide structured frameworks, best practices, and consistent requirements that help improve quality, safety, security, interoperability, and operational effectiveness.
Examples include:
- Management system standards.
- Technical standards.
- Industry standards.
- Product standards.
- Professional standards.
Although many standards are voluntary, they may become mandatory through legislation, regulation, contracts, or customer requirements.
Internal Compliance
Internal compliance focuses on adherence to the policies, standards, procedures, guidelines, and governance requirements established within the entity itself.
Internal requirements often reflect organizational objectives, governance expectations, operational practices, and risk management decisions.
Examples include:
- Organizational policies.
- Standard operating procedures.
- Internal standards.
- Codes of conduct.
- Security policies.
- Quality procedures.
- Operational guidelines.
Internal compliance promotes consistency, accountability, and disciplined execution across the entity.
Ethical Compliance
Ethical compliance extends beyond legal and regulatory obligations by ensuring that decisions and activities align with ethical principles, organizational values, and professional conduct.
Ethical compliance encourages responsible behaviour even where no legal requirement exists.
Examples include:
- Anti-bribery and anti-corruption practices.
- Conflict of interest management.
- Fair competition.
- Responsible use of information.
- Professional ethics.
- Corporate values.
- Responsible business conduct.
Strong ethical compliance enhances organizational integrity, public confidence, and long-term sustainability.
Industry Compliance
Many industries establish common requirements that participating entities are expected to follow to promote consistency, quality, safety, and interoperability.
Industry compliance may be driven by industry associations, professional bodies, sector-specific organizations, or widely accepted industry practices.
Examples include:
- Payment card industry requirements.
- Healthcare industry requirements.
- Aviation industry requirements.
- Telecommunications industry requirements.
- Manufacturing industry requirements.
- Energy sector requirements.
Industry compliance often complements legal and regulatory compliance by addressing sector-specific expectations.
International Compliance
Organizations operating across multiple countries must comply with international obligations in addition to local legal and regulatory requirements.
International compliance requires understanding differences between jurisdictions while maintaining consistent governance and operational practices.
Examples include:
- International treaties.
- Cross-border data protection requirements.
- International trade requirements.
- Global standards.
- Multinational contractual obligations.
Managing international compliance can be challenging due to varying legal systems, regulatory expectations, and cultural considerations.
Importance of Understanding Different Types of Compliance
Entities rarely operate under a single compliance obligation. Most must simultaneously satisfy multiple legal, regulatory, contractual, standards, industry, ethical, and internal requirements.
Understanding these different types of compliance enables entities to:
- Identify applicable obligations.
- Establish effective compliance programs.
- Implement appropriate controls.
- Prioritize compliance activities.
- Reduce legal and regulatory risks.
- Improve operational consistency.
- Strengthen governance and accountability.
- Build stakeholder confidence.
- Support continual improvement.
An effective compliance program integrates these various compliance requirements into a unified governance framework, enabling the entity to meet its obligations efficiently while supporting its strategic and operational objectives.
Audit Lifecycle
An audit follows a structured and systematic process to ensure that audit activities are planned, executed, documented, and completed consistently. Although the scope and complexity of audits vary depending on their objectives, industry, and type, the overall audit lifecycle remains fundamentally the same.
A well-defined audit lifecycle helps ensure that audits are objective, evidence-based, repeatable, and capable of providing reliable assurance to management, governing bodies, regulators, and other stakeholders.
Audit Planning
Audit planning establishes the foundation for a successful audit. During this stage, auditors define the audit objectives, scope, criteria, schedule, resources, and methodology. They also gain an understanding of the processes, systems, and activities that will be evaluated.
Effective planning helps ensure that the audit focuses on the areas of greatest importance and is completed efficiently.
Typical planning activities include:
- Defining audit objectives.
- Establishing the audit scope.
- Identifying audit criteria.
- Reviewing previous audit reports.
- Understanding applicable requirements.
- Assigning audit team members.
- Developing the audit plan.
- Preparing audit checklists.
Audit Preparation
Before fieldwork begins, auditors review relevant documentation and gather background information to understand the environment being audited.
Documentation commonly reviewed includes:
- Policies.
- Standards.
- Procedures.
- Organizational charts.
- Risk assessments.
- Previous audit reports.
- Process documentation.
- Applicable legal and regulatory requirements.
- Management system documentation.
This preparation enables auditors to identify areas that require greater attention during the audit.
Opening Meeting
The audit officially begins with an opening meeting between the audit team and representatives of the audited entity.
The opening meeting is conducted to:
- Introduce the audit team.
- Confirm the audit objectives and scope.
- Explain the audit methodology.
- Review the audit schedule.
- Establish communication channels.
- Address any questions before fieldwork begins.
The meeting helps ensure that all participants have a common understanding of the audit process.
Audit Fieldwork
Audit fieldwork is the stage where auditors collect objective evidence to determine whether activities conform to established requirements.
Evidence may be obtained through:
- Interviews.
- Observations.
- Documentation reviews.
- Record examinations.
- Process walkthroughs.
- Sampling.
- Technical testing.
- Physical inspections.
- System reviews.
Throughout fieldwork, auditors compare collected evidence against the defined audit criteria.
Evidence Collection and Evaluation
Audit conclusions must always be supported by objective and verifiable evidence.
During evaluation, auditors determine whether:
- Activities conform to applicable requirements.
- Controls are properly designed.
- Controls operate effectively.
- Processes achieve their intended objectives.
- Non-conformities exist.
- Improvement opportunities are identified.
Evidence should be sufficient, reliable, relevant, and appropriately documented to support audit conclusions.
Audit Findings
Following the evaluation of evidence, auditors document their findings.
Audit findings generally include:
- Conformities.
- Non-conformities.
- Observations.
- Opportunities for improvement.
- Positive practices.
Each finding should clearly identify:
- The requirement being evaluated.
- The evidence collected.
- The condition observed.
- The significance of the finding.
Well-documented findings provide a sound basis for corrective actions and management decisions.
Closing Meeting
After completing fieldwork, auditors conduct a closing meeting with management and other relevant stakeholders.
The purpose of the closing meeting is to:
- Present preliminary findings.
- Discuss identified non-conformities.
- Clarify observations.
- Resolve factual questions.
- Explain the next steps in the audit process.
The closing meeting ensures that audit results are clearly understood before the final report is issued.
Audit Reporting
The audit report formally documents the outcome of the audit.
A typical audit report includes:
- Audit objectives.
- Audit scope.
- Audit criteria.
- Audit methodology.
- Summary of audit activities.
- Audit findings.
- Non-conformities.
- Opportunities for improvement.
- Conclusions.
- Recommendations.
The audit report provides management and governing bodies with objective information for decision-making and continual improvement.
Corrective Actions
Following the audit, management develops corrective actions to address identified non-conformities and their underlying causes.
Effective corrective actions should:
- Eliminate the root cause.
- Prevent recurrence.
- Strengthen controls.
- Improve processes.
- Address identified weaknesses.
Corrective actions should be assigned, implemented, monitored, and documented until completion.
Follow-up and Audit Closure
The final stage of the audit lifecycle verifies that corrective actions have been effectively implemented.
Follow-up activities confirm that:
- Corrective actions have been completed.
- Root causes have been addressed.
- Controls remain effective.
- Similar issues are unlikely to recur.
Once corrective actions have been verified and the audit objectives have been achieved, the audit is formally closed. The lessons learned from the audit often contribute to future audits and continual improvement initiatives.
Compliance Lifecycle
Compliance is a continuous process rather than a one-time activity. As laws, regulations, standards, contractual obligations, and organizational requirements evolve, compliance activities must also adapt to ensure ongoing conformity.
A structured compliance lifecycle helps entities identify applicable requirements, implement appropriate controls, monitor compliance, address deficiencies, and continually improve their compliance programs.
Identify Compliance Requirements
The first step is identifying all applicable compliance obligations.
These requirements may originate from:
- Laws.
- Regulations.
- Regulatory authorities.
- Industry standards.
- Contractual agreements.
- Organizational policies.
- Governance requirements.
- Professional codes of conduct.
Understanding applicable requirements establishes the foundation of an effective compliance program.
Assess Compliance Obligations
Once identified, compliance requirements are analyzed to determine how they affect operations, products, services, processes, systems, and personnel.
This assessment helps determine:
- Applicable business functions.
- Required controls.
- Documentation requirements.
- Reporting obligations.
- Resource needs.
- Compliance priorities.
Develop Policies and Procedures
Compliance requirements are translated into operational practices through policies, standards, procedures, guidelines, and supporting documentation.
These documents define:
- Responsibilities.
- Operational requirements.
- Control expectations.
- Reporting processes.
- Monitoring activities.
Well-defined documentation promotes consistent implementation throughout the entity.
Implement Compliance Controls
Compliance requirements are implemented through appropriate administrative, technical, and physical controls.
Examples include:
- Access controls.
- Approval workflows.
- Employee awareness programs.
- Security controls.
- Operational procedures.
- Record management.
- Monitoring mechanisms.
Implementation ensures that compliance requirements become part of routine operations.
Monitor Compliance
Compliance should be continuously monitored to verify ongoing conformity.
Monitoring activities may include:
- Internal reviews.
- Compliance assessments.
- Control testing.
- Performance metrics.
- Exception reporting.
- Continuous monitoring technologies.
Continuous monitoring enables early detection of compliance issues before they become significant problems.
Manage Non-Conformities
When non-conformities are identified, they should be documented, investigated, and addressed promptly.
Managing non-conformities involves:
- Recording the issue.
- Determining the root cause.
- Implementing corrective actions.
- Verifying effectiveness.
- Preventing recurrence.
Effective management of non-conformities strengthens the overall compliance program.
Review and Report
Compliance activities should be periodically reviewed and reported to management and governing bodies.
Reports commonly include:
- Compliance status.
- Significant findings.
- Outstanding issues.
- Regulatory developments.
- Corrective action status.
- Emerging compliance risks.
Regular reporting supports effective oversight and informed decision-making.
Continual Improvement
Compliance programs should continually evolve to address changing legal, regulatory, technological, operational, and business requirements.
Continual improvement may involve:
- Updating policies.
- Improving controls.
- Enhancing monitoring.
- Refining procedures.
- Strengthening employee awareness.
- Incorporating lessons learned.
A mature compliance program continuously adapts while maintaining conformity with applicable requirements and supporting long-term organizational objectives.
Internal Controls and Their Importance
Internal controls are policies, procedures, practices, and mechanisms established to provide reasonable assurance that activities are performed as intended, objectives are achieved, risks are appropriately managed, assets are protected, and applicable requirements are consistently satisfied. They are a fundamental component of governance, risk management, audit, and compliance across public and private sectors.
Internal controls are applicable to every discipline, including finance, information technology, cybersecurity, quality management, healthcare, manufacturing, critical infrastructure, government, education, and environmental management. Regardless of the industry or operational environment, effective controls help improve consistency, reliability, accountability, and resilience.
Audit and compliance rely on internal controls to determine whether activities are operating effectively and in accordance with established requirements. Compliance focuses on ensuring that required controls are implemented and maintained, while audit independently evaluates whether those controls are appropriately designed, effectively implemented, and operating as intended.
Internal controls do not eliminate risk. Instead, they reduce the likelihood and impact of undesirable events to an acceptable level while supporting the achievement of strategic, operational, financial, and regulatory objectives.
Objectives of Internal Controls
Internal controls are implemented to:
- Protect assets and resources.
- Achieve strategic and operational objectives.
- Ensure reliable information and reporting.
- Reduce risks and uncertainties.
- Prevent fraud, errors, and misuse.
- Support legal, regulatory, and contractual compliance.
- Improve operational consistency.
- Strengthen accountability and transparency.
- Support effective governance.
- Promote continual improvement.
Categories of Internal Controls
Internal controls are commonly classified into three broad categories.
Administrative Controls
Administrative controls establish the governance structure, policies, procedures, responsibilities, and management practices that direct how activities should be performed.
Examples include:
- Policies and procedures.
- Organizational structures.
- Segregation of duties.
- Risk assessments.
- Change management.
- Vendor management.
- Employee awareness and training.
- Approval and authorization processes.
Administrative controls provide the management foundation for consistent and accountable operations.
Technical Controls
Technical controls use technology to protect information, systems, networks, and digital assets while supporting secure and reliable operations.
Examples include:
- Authentication mechanisms.
- Access control systems.
- Encryption.
- Firewalls.
- Endpoint protection.
- Security monitoring.
- Backup solutions.
- Logging and audit trails.
Technical controls help maintain confidentiality, integrity, availability, and operational reliability.
Physical Controls
Physical controls protect people, facilities, equipment, and physical assets from unauthorized access, damage, theft, or environmental hazards.
Examples include:
- Physical locks.
- Access cards.
- Security guards.
- CCTV systems.
- Visitor management.
- Perimeter fencing.
- Fire detection and suppression systems.
- Environmental monitoring systems.
Physical controls complement administrative and technical controls by securing the physical environment.
Functional Classification of Internal Controls
Internal controls may also be classified according to the function they perform.
Preventive Controls
Preventive controls are designed to stop undesirable events before they occur.
Examples include:
- Access authorization.
- Multi-factor authentication.
- Segregation of duties.
- Security awareness training.
- Approval workflows.
Detective Controls
Detective controls identify incidents, errors, policy violations, or control failures after they occur.
Examples include:
- Security monitoring.
- Log reviews.
- Internal audits.
- CCTV monitoring.
- Exception reporting.
- Reconciliations.
Corrective Controls
Corrective controls restore normal operations after an issue has been identified.
Examples include:
- Corrective actions.
- Incident response.
- Patch management.
- System recovery.
- Restoring backups.
Directive Controls
Directive controls provide guidance on how activities should be performed to achieve desired outcomes.
Examples include:
- Policies.
- Standards.
- Procedures.
- Guidelines.
- Codes of conduct.
Deterrent Controls
Deterrent controls discourage inappropriate or unauthorized behaviour.
Examples include:
- Warning notices.
- Visible surveillance.
- Security personnel.
- Security awareness programs.
- Disciplinary policies.
Compensating Controls
Compensating controls provide alternative safeguards when a primary control cannot be implemented or is temporarily unavailable.
They should provide protection that is comparable to the original control while maintaining an acceptable level of risk.
Recovery Controls
Recovery controls restore systems, services, operations, or data following disruptions or incidents.
Examples include:
- Disaster recovery plans.
- Business continuity procedures.
- Backup restoration.
- System redundancy.
- Emergency response procedures.
Characteristics of Effective Internal Controls
Effective internal controls should be:
- Appropriate.
- Risk-based.
- Clearly documented.
- Consistently implemented.
- Measurable.
- Cost-effective.
- Regularly monitored.
- Periodically reviewed.
- Continually improved.
Well-designed internal controls improve operational reliability, reduce uncertainty, strengthen governance, and increase confidence that objectives can be achieved effectively.
Audit Evidence and Documentation
The credibility of an audit depends on the quality of the evidence collected and the documentation used to support audit conclusions. Audit findings should always be based on objective, verifiable, and sufficient evidence rather than assumptions, opinions, or personal judgement.
Evidence enables auditors to determine whether activities conform to established requirements, whether controls operate effectively, and whether management systems achieve their intended objectives. Documentation records the audit process and provides a permanent record of the evidence, observations, findings, and conclusions.
What is Audit Evidence?
Audit evidence is any information collected during an audit that supports audit findings and conclusions. It enables auditors to determine whether audit criteria have been satisfied and whether sufficient assurance can be provided regarding the activities being evaluated.
Evidence may exist in physical, electronic, verbal, or observational forms and should always be relevant to the audit objectives.
Characteristics of Audit Evidence
Audit evidence should be:
- Sufficient
- Appropriate
- Relevant
- Reliable
- Objective
- Verifiable
- Complete
- Traceable
Evidence that does not possess these characteristics may weaken audit conclusions and reduce confidence in the audit.
Sources of Audit Evidence
Audit evidence may be obtained from numerous sources, including:
- Policies
- Standards
- Procedures
- Contracts
- Records
- Risk assessments
- Financial records
- System logs
- Configuration settings
- Incident reports
- Training records
- Monitoring reports
- Physical observations
- Interviews
- Technical testing
- Photographs and recordings
Using multiple sources of evidence increases the reliability and credibility of audit findings.
Methods of Collecting Audit Evidence
Auditors use various techniques to obtain sufficient and appropriate evidence.
Common methods include:
- Interviews
- Observation
- Inspection
- Documentation review
- Sampling
- Technical testing
- Process walkthroughs
- Data analysis
- Analytical procedures
The selection of evidence collection methods depends on the audit objectives, scope, audit criteria, and the level of assurance required.
Audit Documentation
Audit documentation records the planning, execution, evidence collection, findings, and conclusions of an audit. It demonstrates that the audit was performed systematically and in accordance with established audit principles.
Typical audit documentation includes:
- Audit plans
- Audit scope and objectives
- Audit checklists
- Working papers
- Interview notes
- Evidence records
- Observation records
- Sampling results
- Audit findings
- Corrective action records
- Audit reports
Well-maintained documentation supports transparency, repeatability, accountability, and future audits.
Importance of Audit Evidence and Documentation
High-quality audit evidence and documentation are essential because they:
- Support objective audit conclusions
- Demonstrate conformity with audit criteria
- Improve transparency and accountability
- Enable independent verification
- Support corrective actions
- Facilitate future audits
- Increase stakeholder confidence
- Promote continual improvement
Without sufficient evidence and appropriate documentation, audit findings cannot be adequately substantiated, reducing the credibility, reliability, and value of the audit process.
Roles and Responsibilities in Audit and Compliance
Audit and compliance involve multiple stakeholders working together to ensure that applicable requirements are implemented, monitored, evaluated, and continually improved. Although responsibilities vary depending on the governance structure, regulatory environment, and operational model, every stakeholder has a role in maintaining accountability, transparency, and assurance.
Audit provides independent assurance regarding the effectiveness of governance, risk management, internal controls, and compliance activities, while compliance focuses on implementing and maintaining conformity with applicable requirements. Achieving these objectives requires collaboration among governing bodies, leadership, management, auditors, compliance professionals, process owners, employees, and external parties.
Governing Bodies
Governing bodies provide oversight and strategic direction for audit and compliance activities. They establish expectations for accountability, integrity, ethical conduct, and effective governance while ensuring that adequate resources and authority are available.
Typical responsibilities include:
- Providing governance oversight.
- Approving audit and compliance strategies.
- Reviewing significant audit findings.
- Monitoring compliance performance.
- Ensuring accountability.
- Supporting continual improvement.
Executive Leadership
Executive leadership is responsible for implementing governance decisions and fostering a culture of accountability, integrity, and compliance throughout the entity.
Key responsibilities include:
- Supporting audit and compliance programs.
- Allocating appropriate resources.
- Implementing governance decisions.
- Monitoring performance.
- Reviewing significant risks and issues.
- Ensuring corrective actions are completed.
Audit Function
The audit function independently evaluates governance, risk management, internal controls, and operational activities to provide objective assurance.
Its primary responsibilities include:
- Developing audit plans.
- Conducting independent audits.
- Collecting and evaluating evidence.
- Identifying non-conformities.
- Reporting audit findings.
- Recommending improvements.
- Verifying corrective actions.
The audit function should remain independent of the activities it evaluates to preserve objectivity and credibility.
Compliance Function
The compliance function establishes and maintains processes that help ensure conformity with applicable legal, regulatory, contractual, industry, and internal requirements.
Typical responsibilities include:
- Identifying applicable requirements.
- Developing compliance policies and procedures.
- Monitoring compliance activities.
- Providing compliance guidance.
- Supporting awareness and training.
- Managing compliance reporting.
- Coordinating corrective actions.
Compliance functions often work closely with operational teams while maintaining oversight responsibilities.
Process and Control Owners
Process and control owners are responsible for implementing, operating, and maintaining the controls and processes assigned to them.
Their responsibilities typically include:
- Implementing approved controls.
- Maintaining required documentation.
- Monitoring process performance.
- Addressing identified issues.
- Supporting audits and assessments.
- Implementing corrective actions.
They play a critical role in ensuring that controls remain effective during normal operations.
Employees and Personnel
Every individual contributes to audit and compliance by performing assigned responsibilities in accordance with established policies, procedures, standards, and applicable requirements.
Responsibilities include:
- Following established procedures.
- Protecting information and assets.
- Reporting incidents and non-conformities.
- Maintaining accurate records.
- Participating in awareness and training.
- Supporting audit activities when required.
Audit and compliance are collective responsibilities rather than functions performed by a single department.
External Auditors
External auditors provide independent assurance to customers, regulators, certification bodies, investors, governing bodies, or other interested parties.
Their responsibilities include:
- Conducting impartial assessments.
- Evaluating conformity with audit criteria.
- Reporting objective findings.
- Providing independent assurance.
- Supporting certifications or regulatory requirements.
Because external auditors remain independent of the audited activities, their assessments often provide greater confidence to external stakeholders.
Regulators and Oversight Authorities
Regulatory and oversight authorities establish requirements, monitor compliance, conduct inspections, and enforce applicable laws and regulations within their respective jurisdictions.
Depending on the sector, their responsibilities may include:
- Issuing regulatory requirements.
- Conducting inspections.
- Reviewing compliance reports.
- Investigating violations.
- Taking enforcement actions.
- Promoting public confidence.
Shared Responsibility for Audit and Compliance
Effective audit and compliance depend on cooperation across all levels and functions. While audit provides independent assurance and compliance maintains conformity, successful implementation requires participation from leadership, management, operational personnel, auditors, compliance professionals, regulators, and other stakeholders.
Clearly defined roles and responsibilities improve accountability, strengthen governance, reduce risk, and support continual improvement across all activities.
Common Audit and Compliance Frameworks and Standards
Audit and compliance activities are guided by internationally recognized frameworks, standards, regulations, and professional practices. These provide structured approaches for establishing governance, managing risks, implementing controls, conducting audits, maintaining compliance, and demonstrating accountability.
Although different frameworks serve different purposes, they share common objectives such as improving consistency, strengthening assurance, supporting continual improvement, and promoting effective governance.
ISO Management System Standards
The International Organization for Standardization (ISO) publishes internationally recognized management system standards that establish requirements and guidance for governance, risk management, operational processes, and continual improvement.
Examples include:
- ISO 9001 – Quality Management Systems.
- ISO/IEC 27001 – Information Security Management Systems.
- ISO 14001 – Environmental Management Systems.
- ISO 22301 – Business Continuity Management Systems.
- ISO 45001 – Occupational Health and Safety Management Systems.
These standards provide a structured foundation for both audit and compliance activities.
ISO 19011
ISO 19011 provides guidance for auditing management systems. It establishes widely accepted auditing principles and guidance on managing audit programs, conducting audits, evaluating auditor competence, and reporting audit results.
It is one of the most widely referenced standards for internal and external management system audits.
COSO Internal Control Framework
The COSO Internal Control Framework provides guidance for designing, implementing, evaluating, and improving internal controls.
It helps strengthen governance, improve risk management, support reliable reporting, and enhance operational effectiveness through an integrated system of internal controls.
COBIT
COBIT provides a governance and management framework for enterprise information and technology. It helps align technology with business objectives while supporting governance, risk management, audit, compliance, and performance measurement.
COBIT is widely used for information technology governance and IT audits.
Regulatory Frameworks
Many sectors operate under regulatory frameworks established by government authorities or industry regulators.
Examples include regulations relating to:
- Financial services.
- Healthcare.
- Telecommunications.
- Energy.
- Aviation.
- Data protection.
- Environmental protection.
Compliance with these frameworks is often mandatory and subject to regulatory oversight.
Industry Frameworks
Many industries establish common frameworks and best practices to improve consistency, quality, safety, and operational performance.
Examples include cybersecurity frameworks, payment security frameworks, quality frameworks, and sector-specific operational frameworks.
Industry frameworks often complement legal and regulatory requirements.
Professional Guidance
Professional bodies publish guidance that supports auditors and compliance professionals in applying recognized practices.
These publications commonly address:
- Audit methodologies.
- Professional ethics.
- Auditor competence.
- Risk-based auditing.
- Evidence collection.
- Reporting practices.
Professional guidance complements formal standards by providing practical implementation advice.
Selecting Appropriate Frameworks
The choice of framework depends on several factors, including:
- Applicable legal and regulatory requirements.
- Industry expectations.
- Operational objectives.
- Risk profile.
- Nature of activities.
- Contractual obligations.
- Stakeholder expectations.
Many entities adopt multiple frameworks simultaneously to satisfy different governance, operational, and compliance requirements.
By applying recognized frameworks and standards, audit and compliance activities become more structured, consistent, transparent, and effective, while improving confidence among governing bodies, regulators, customers, and other stakeholders.
Audit and Compliance Best Practices
Effective audit and compliance programs are built upon recognized principles, structured processes, competent personnel, and a commitment to continual improvement. While implementation approaches vary across different sectors and operational environments, several best practices consistently contribute to successful audit and compliance outcomes.
Establish Clear Governance
Clearly defined governance structures help ensure accountability, oversight, decision-making authority, and effective coordination between audit, compliance, management, and governing bodies.
Roles, responsibilities, and reporting relationships should be formally documented and regularly reviewed.
Adopt a Risk-Based Approach
Audit and compliance activities should prioritize areas that present the greatest level of risk, regulatory significance, or operational impact.
A risk-based approach enables resources to be focused where they provide the greatest value and assurance.
Maintain Current Policies and Procedures
Policies, standards, procedures, and supporting documentation should remain accurate, relevant, and aligned with current legal, regulatory, contractual, and operational requirements.
Regular reviews help ensure continued effectiveness.
Strengthen Internal Controls
Effective internal controls provide the foundation for successful audit and compliance programs.
Controls should be appropriately designed, consistently implemented, periodically evaluated, and continually improved to address changing risks and operational requirements.
Promote Awareness and Competence
Audit and compliance depend upon knowledgeable and competent personnel.
Regular awareness programs, professional development, and role-based training help ensure that responsibilities are understood and consistently performed.
Use Reliable Evidence
Audit conclusions should always be supported by sufficient, appropriate, objective, and verifiable evidence.
Evidence should be collected systematically, documented appropriately, and retained according to applicable requirements.
Leverage Technology
Modern technologies can improve the efficiency, consistency, and effectiveness of audit and compliance activities.
Examples include:
- Governance, Risk, and Compliance (GRC) platforms.
- Continuous monitoring solutions.
- Data analytics.
- Automation.
- Artificial intelligence.
- Workflow management tools.
Technology should enhance professional judgement rather than replace it.
Monitor and Measure Performance
Regular monitoring enables management to evaluate whether audit and compliance activities continue to achieve their intended objectives.
Performance may be measured using:
- Key Performance Indicators (KPIs).
- Key Risk Indicators (KRIs).
- Audit findings.
- Compliance metrics.
- Corrective action completion rates.
- Maturity assessments.
Measurement supports continual improvement and informed decision-making.
Encourage Continual Improvement
Audit and compliance should continually evolve in response to changes in regulations, technologies, operational practices, stakeholder expectations, and emerging risks.
Lessons learned from audits, incidents, assessments, and corrective actions should be incorporated into future improvements.
Foster an Ethical Culture
Successful audit and compliance programs depend on integrity, accountability, transparency, and ethical behaviour at every level.
An environment that encourages openness, responsible decision-making, and timely reporting of concerns strengthens governance and supports sustainable long-term performance.
By adopting these best practices, entities can strengthen governance, improve operational performance, enhance stakeholder confidence, reduce risk, and establish audit and compliance programs that remain effective in an evolving regulatory and operational environment.
Conclusion
Audit and compliance are fundamental disciplines that provide assurance, accountability, and confidence across governance, operations, financial management, information technology, cybersecurity, quality management, healthcare, manufacturing, critical infrastructure, government, education, and many other sectors.
Although audit and compliance have distinct responsibilities, they work together to ensure that applicable requirements are implemented, monitored, evaluated, and continually improved. Compliance establishes and maintains conformity with legal, regulatory, contractual, industry, and internal requirements, while audit independently evaluates the effectiveness of governance, risk management, internal controls, and compliance activities.
Throughout this article, we explored the principles, objectives, roles, types, lifecycles, controls, evidence, frameworks, challenges, and emerging trends that define modern audit and compliance. Together, these concepts provide a structured approach for improving accountability, strengthening governance, supporting effective risk management, enhancing operational performance, and promoting continual improvement.
As operational environments become more interconnected and regulatory expectations continue to evolve, audit and compliance will remain essential for maintaining trust, transparency, resilience, and responsible decision-making. While technologies such as artificial intelligence, automation, continuous monitoring, and data analytics will transform how assurance activities are performed, the core principles of independence, objectivity, integrity, and evidence-based evaluation will continue to define the profession.
A well-designed audit and compliance program is more than a mechanism for identifying deficiencies or satisfying regulatory obligations. It is a strategic capability that supports informed decision-making, improves performance, strengthens stakeholder confidence, and contributes to the long-term success and sustainability of any entity.
References
Online Sources
The Institute of Internal Auditors (IIA) – Global Internal Audit Standards
Provides professional standards for internal auditing, covering ethics, governance of the audit function, audit planning, engagement execution, reporting, and follow-up.
ISO – ISO 19011:2026 – Guidelines for Auditing Management Systems
Provides guidance on audit principles, audit programme management, conducting management system audits, and auditor competence.
ISO – ISO 37301:2021 – Compliance Management Systems
Specifies requirements and provides guidance for establishing, implementing, evaluating, maintaining, and improving compliance management systems.
COSO – Internal Control—Integrated Framework
Provides a framework for designing, implementing, and evaluating internal controls to support organizational objectives, reliable information, and compliance.
U.S. Government Accountability Office (GAO) – Government Auditing Standards (Yellow Book)
Provides auditing standards for government entities and organizations conducting audits under applicable government auditing requirements, including financial, attestation, and performance audits.
ISACA – COBIT Framework
Provides a framework for the governance and management of enterprise information and technology, including governance objectives, management practices, and control-related guidance.
ISACA – IT Audit Framework (ITAF)
Provides professional standards and guidance for IT audit and assurance, including practitioner responsibilities, engagement planning, audit execution, evidence, and reporting.