Understanding Known and Unknown in Cybersecurity
Introduction
Every decision is made with incomplete information. Individuals, governments, enterprises, military forces, critical infrastructure operators, scientific communities, and society must act based on what they know, what they recognize they do not know, and what they have not yet considered. The quality of a decision depends not only on the information available but also on the ability to understand its limitations.
The concept of known and unknown provides a way to examine knowledge, uncertainty, assumptions, and information gaps. It helps explain why some situations can be planned for with confidence, why others require further investigation, and why unexpected events can create serious consequences.
In cybersecurity, this concept is especially useful. Security teams may know which systems exist, which vulnerabilities have been identified, and which threats have been observed. However, they may also be unaware of undocumented assets, undiscovered vulnerabilities, overlooked intelligence, or attack methods that have not yet been encountered. A security program that considers only known information can therefore create a false sense of assurance.
Understanding known and unknown helps individuals, governments, enterprises, military forces, critical infrastructure operators, scientific communities, and society improve situational awareness, challenge assumptions, identify information gaps, prepare for unexpected conditions, and make better-informed decisions. It does not eliminate uncertainty, but it provides a structured way to recognize and manage it.
The Origin of Known and Unknown
The Historical Context
The concept of known and unknown comes from the recognition that human knowledge is incomplete. Individuals and institutions often make decisions using available information while facing information gaps, uncertain conditions, and events that have not been anticipated.
This idea is relevant to science, government, military operations, enterprises, critical infrastructure, risk management, crisis management, and cybersecurity. In each area, decisions depend on understanding what is known, recognizing what is uncertain, and preparing for what may not yet be understood.
Donald Rumsfeld’s 2002 Explanation
On February 12, 2002, U.S. Secretary of Defense Donald Rumsfeld discussed the concepts during a Department of Defense briefing concerning war, military operations, national security, and intelligence information. His explanation brought wider attention to the relationship between knowledge, uncertainty, and decision-making.
Rumsfeld explained that some information is known and understood, some information gaps are recognized, and some possibilities remain outside current awareness. His comments were made in the context of military and national security decision-making, where incomplete intelligence can affect planning, assessments, and operational choices.
War, Military Operations, and National Security
War and military operations demonstrate the importance of distinguishing between confirmed information, recognized uncertainty, and possibilities that have not yet been identified. Military leaders may know the location of certain forces, understand established capabilities, or recognize specific intelligence gaps. However, they may not know an opponent’s intentions, future actions, hidden capabilities, or the consequences of a particular decision.
This uncertainty can be influenced by deception, incomplete intelligence, changing conditions, communication failures, and the difficulty of predicting human decisions. As a result, military planning must account for both available knowledge and the possibility of unexpected developments.
The Limits of Knowledge
The concept also highlights the limits of intelligence and analysis. Information may be incomplete, inaccurate, outdated, misunderstood, or unavailable. Even when information exists, decision-makers may fail to recognize its importance or may interpret it through existing assumptions.
Recognizing these limitations encourages a careful approach to planning. It promotes the use of multiple sources, alternative scenarios, continuous assessment, and clear documentation of assumptions. The objective is not to achieve complete knowledge, which is rarely possible, but to reduce avoidable uncertainty and improve the quality of decisions.
Why the Concepts Became Widely Used
The concepts became widely used because they describe a common problem across different fields: people must make decisions without having complete knowledge of the situation. Their simplicity makes them useful for discussing risk, uncertainty, intelligence, planning, and preparedness.
Although the concepts became widely associated with Rumsfeld’s 2002 explanation, the underlying idea is not limited to military operations. It can also be applied to scientific research, public policy, business strategy, critical infrastructure resilience, crisis management, and cybersecurity.
The Four Categories of Knowledge and Uncertainty
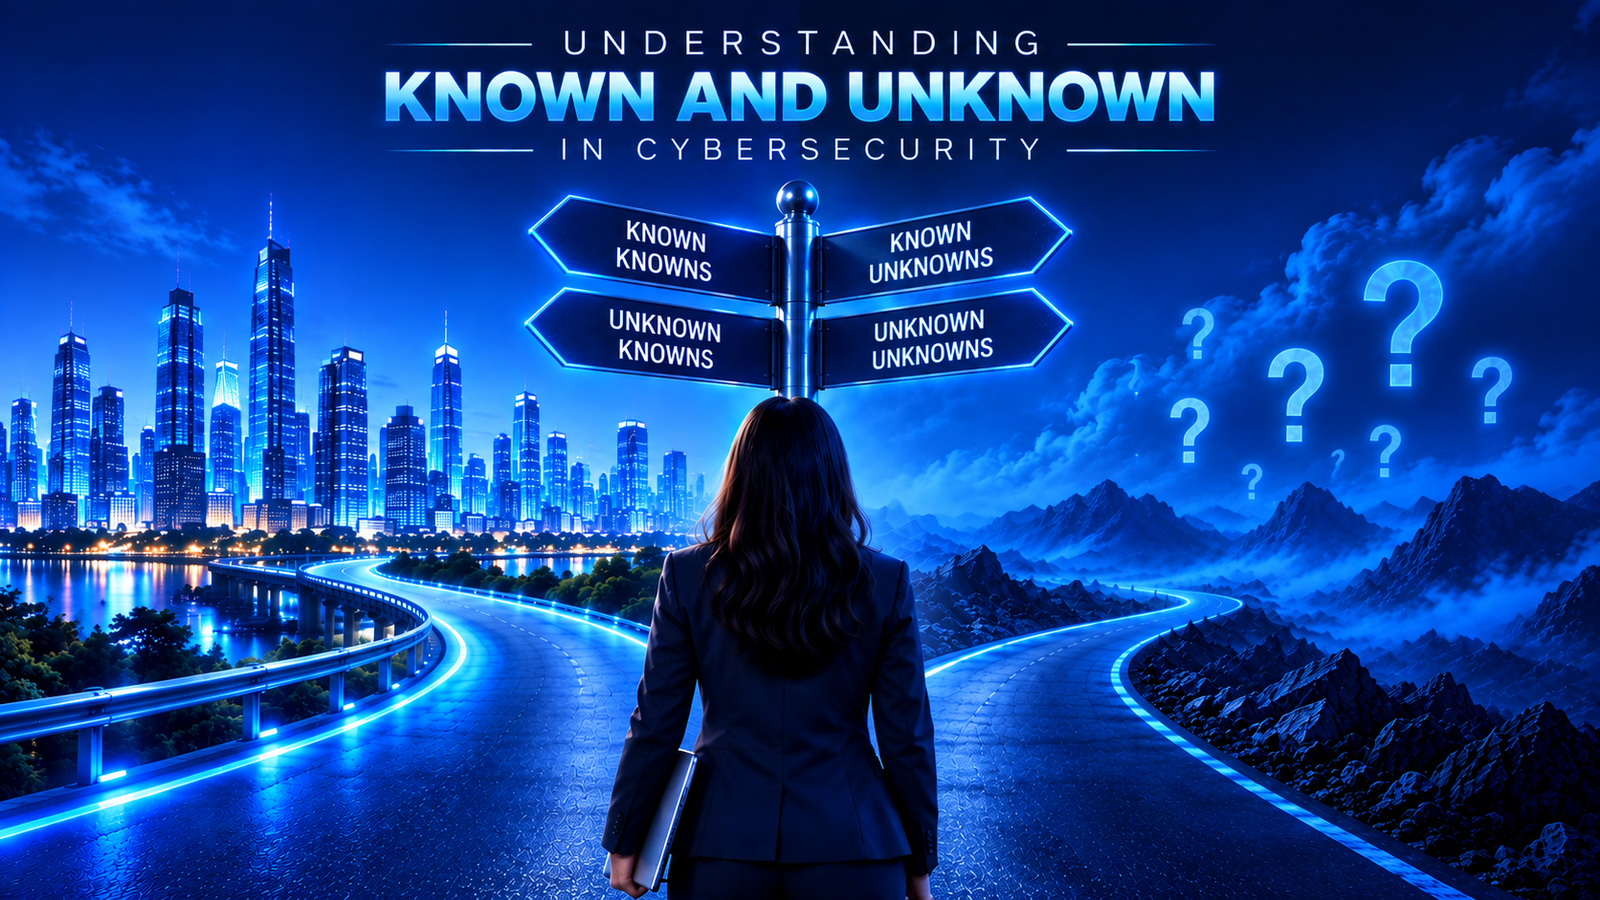
Donald Rumsfeld’s 2002 explanation referred to three categories of knowledge and uncertainty: known knowns, known unknowns, and unknown unknowns. The category of unknown knowns was introduced later by analysts and commentators to describe information that exists but is overlooked, unrecognized, or not properly understood.
The original three-part explanation and the later four-part model are therefore different. The expanded four-category model is commonly called the Rumsfeld Matrix and provides a broader way to examine knowledge, uncertainty, hidden information, and unexpected conditions.
Known Knowns
Known knowns are facts, conditions, or information that are available, recognized, and understood by the people making a decision. They represent the established knowledge on which planning, analysis, and action can be based.
Known knowns may come from direct observation, reliable records, validated research, monitoring systems, documented procedures, or previous experience. They provide a foundation for decisions because the information has already been identified and interpreted.
However, known knowns are not necessarily permanent or completely accurate. Information that was once correct may become outdated, and information that appears reliable may contain errors. Therefore, known knowns should still be reviewed, validated, and updated when conditions change.
Examples include documented systems, confirmed scientific findings, established procedures, identified infrastructure dependencies, and verified cybersecurity vulnerabilities.
In cybersecurity, known knowns may include an approved asset inventory, documented network architecture, identified user accounts, confirmed security controls, recorded vulnerabilities, and previously observed attack techniques. These facts help security teams understand the environment and determine where protection is required.
Known Unknowns
Known unknowns are information gaps that have already been recognized. A person or institution knows that something is not understood, but the specific answer is not yet available.
These uncertainties are often easier to manage than unknown unknowns because the missing information has already been identified. Once an information gap is recognized, it can be assigned for investigation, measurement, monitoring, testing, or further analysis.
Known unknowns may involve missing data, uncertain intentions, incomplete technical knowledge, unresolved causes, or conditions that cannot yet be predicted with confidence. Recognizing them helps prevent decision-makers from treating assumptions as established facts.
Examples include an unresolved scientific question, an uncertain military capability, an unidentified cause of a system failure, an unknown business dependency, or a vulnerability that may exist but has not yet been discovered.
In cybersecurity, known unknowns may include uncertainty about whether an undocumented asset exists, whether a threat actor has gained access, whether a vulnerability is exploitable in a particular environment, or whether an alert represents a genuine attack. These gaps require investigation and should be recorded rather than ignored.
Unknown Knowns
Unknown knowns are facts or information that exist but are not recognized, remembered, shared, or properly understood by the people making a decision.
The information may be stored in documents, systems, reports, personal experience, or another department, but it is not connected to the decision-making process. In some cases, the information is available but overlooked. In other cases, it may be misunderstood, poorly communicated, or separated from the people who need it.
Unknown knowns often result from knowledge silos, weak documentation, poor communication, organizational changes, incomplete handovers, or excessive dependence on individual employees. They demonstrate that the existence of information does not guarantee that it will be used effectively.
Examples include undocumented operational knowledge, information held by another department, overlooked intelligence, forgotten lessons from previous incidents, or security findings that were recorded but never reviewed.
In cybersecurity, an unknown known may be a vulnerability identified by one team but not communicated to the system owner, an earlier incident report that contains relevant warning signs, or a firewall rule known to an administrator but absent from the official network documentation.
Unknown Unknowns
Unknown unknowns are conditions, events, or possibilities that have not been identified and are not currently recognized as information gaps.
Because they have not been anticipated, decision-makers may not know that they should investigate them, prepare for them, or include them in planning. This makes unknown unknowns particularly difficult to address through traditional risk assessment and forecasting.
Unknown unknowns may arise from unexpected interactions, emerging technologies, changing human behavior, hidden dependencies, rare events, or conditions that fall outside existing assumptions. They do not always represent completely unforeseeable events; sometimes they become visible only after an existing model, process, or assumption has failed.
Examples include unexpected technological failures, new forms of attack, unforeseen consequences of a conflict, rare natural events, or disruptions caused by previously unrecognized dependencies.
In cybersecurity, unknown unknowns may include a previously unseen attack technique, an unexpected interaction between systems, a new vulnerability class, or an attack path that was not considered during security assessment. Security teams cannot identify every unknown unknown in advance, but they can improve resilience through layered controls, continuous monitoring, incident response, threat intelligence, scenario analysis, testing, and adaptable recovery plans.
Known and Unknown in Cybersecurity
Cybersecurity decisions are made using a combination of established facts, recognized information gaps, overlooked information, and unexpected conditions. Security teams may have detailed knowledge of their systems and controls, but that knowledge is never complete. Assets may be undocumented, vulnerabilities may remain undiscovered, threat intelligence may be misunderstood, and attackers may use methods that have not previously been observed.
The concepts of known knowns, known unknowns, unknown knowns, and unknown unknowns provide a useful way to examine these conditions. They help security teams distinguish between what has been confirmed, what requires investigation, what information already exists but has not been recognized, and what may emerge outside existing assumptions.
Known and Unknown Threats
Known threats are threats that have already been identified through threat intelligence, previous incidents, security research, vulnerability disclosures, or established attack patterns. Examples include phishing, ransomware, credential theft, denial-of-service attacks, malware, and exploitation of known vulnerabilities.
Security teams can prepare for known threats by documenting their characteristics, identifying affected assets, applying security controls, monitoring relevant indicators, and developing response procedures.
Unknown threats are threats that have not yet been identified or sufficiently understood. They may involve new attack methods, previously unseen combinations of techniques, emerging threat actors, or changes in attacker behaviour.
A threat may also be unknown because the organization has not collected enough information to recognize it. For example, an organization may not know that a particular business process is being targeted or that an attacker is using a previously overlooked route into the environment.
Threat intelligence helps reduce this uncertainty by collecting, analyzing, and sharing information about adversaries, capabilities, intentions, infrastructure, and attack methods. However, threat intelligence cannot identify every threat in advance.
Known and Unknown Cyberattacks
Known cyberattacks are attacks that have been observed, documented, analyzed, or classified. Security teams may recognize the attack method through indicators such as malicious files, suspicious network traffic, unusual authentication activity, known command patterns, or previously identified attacker infrastructure.
Examples include:
- Phishing campaigns using known malicious domains.
- Ransomware attacks using established techniques.
- Credential attacks against exposed services.
- Exploitation of publicly disclosed vulnerabilities.
- Distributed denial-of-service attacks.
- Malware associated with a known threat group.
Known attacks can be addressed through prevention, detection, response, and recovery measures. Security monitoring rules, endpoint protections, network controls, incident response procedures, and threat intelligence feeds can all support this process.
Unknown cyberattacks may use new techniques, unfamiliar infrastructure, previously unseen malware, or combinations of legitimate tools that do not match existing detection rules. An attack may also remain unknown because its indicators are too subtle, its activity is hidden within normal operations, or the organization lacks sufficient visibility.
The absence of a detected attack does not necessarily prove that no attack has occurred. Limited logging, incomplete monitoring, poor visibility, and incorrect assumptions can prevent an organization from recognizing malicious activity. Rumsfeld expressed a similar principle in the context of intelligence: the absence of evidence is not necessarily evidence of absence.
Known and Unknown Vulnerabilities
Known vulnerabilities are weaknesses that have been identified through security research, vendor advisories, vulnerability assessments, penetration testing, code review, configuration reviews, or incident investigations.
Examples include:
- Unpatched software vulnerabilities.
- Weak authentication mechanisms.
- Excessive privileges.
- Insecure configurations.
- Exposed administrative interfaces.
- Unsupported operating systems.
- Inadequate input validation.
- Incorrect access-control rules.
Known vulnerabilities can be recorded in vulnerability management systems, assigned to responsible owners, prioritized according to risk, and addressed through remediation or compensating controls.
Unknown vulnerabilities are weaknesses that have not yet been discovered or recognized. They may exist in software, hardware, configurations, applications, cloud services, identity systems, or operational processes.
A vulnerability may remain unknown because:
- The relevant code or configuration has not been reviewed.
- The affected system is not included in the asset inventory.
- The weakness requires a rare combination of conditions.
- Security testing did not cover the relevant attack path.
- The vulnerability has not yet been publicly disclosed.
- The organization lacks sufficient technical visibility.
Unknown vulnerabilities cannot be eliminated completely. Organizations can reduce their exposure through secure development practices, vulnerability management, configuration management, threat modeling, continuous monitoring, security testing, patch management, and layered controls.
Known and Unknown Risks
Known risks are risks that have been identified and assessed. They may be recorded in a risk register or discussed during security reviews, governance meetings, business impact assessments, and continuity planning.
Examples include:
- A critical application depending on a single server.
- An administrator account without strong authentication.
- A supplier with inadequate security controls.
- An unsupported operating system.
- A network connection without sufficient protection.
- A lack of tested recovery procedures.
- A known vulnerability affecting an important business service.
Known risks can be evaluated according to their likelihood, impact, exposure, and existing controls. Management can then decide whether to reduce, transfer, avoid, accept, or monitor the risk.
Unknown risks are risks that have not been identified or considered. They may arise from unexpected dependencies, changes in technology, new business arrangements, emerging threats, human behaviour, or interactions between systems.
For example, an organization may understand the risks associated with an individual application but fail to recognize that the application shares an identity service with several critical systems. A failure in that shared service could therefore create a wider impact than originally expected.
Unknown risks become more visible when assumptions are challenged, new information is discovered, or an unexpected event occurs. Risk management should therefore not be treated as a one-time exercise. Risk assessments should be reviewed when systems, suppliers, business processes, threats, or operating conditions change.
Known and Unknown Security Gaps
Known security gaps are weaknesses in the existing security program that have already been identified. They may involve technology, people, processes, governance, documentation, or operational practices.
Examples include:
- Missing security controls.
- Incomplete asset inventories.
- Weak security policies.
- Insufficient logging.
- Lack of security awareness training.
- Unclear incident response responsibilities.
- Inadequate network segmentation.
- Incomplete backup testing.
- Delayed vulnerability remediation.
Known gaps can be documented in audit findings, risk registers, security assessment reports, compliance reviews, and improvement plans. Their importance depends on the systems affected, the threat environment, the likelihood of exploitation, and the potential business impact.
Unknown security gaps are weaknesses that have not been identified. They may exist because a control has never been assessed, a process is not documented, or the organization assumes that a control operates effectively without verifying it.
For example, an organization may believe that all privileged accounts are monitored, while a recently introduced cloud service uses a separate administrative identity system that is not included in the monitoring process.
Security assurance activities help reduce unknown gaps. These activities include independent assessments, control testing, architecture reviews, configuration reviews, internal audits, incident lessons learned, and continuous improvement.
Known and Unknown Threat Actors
Known threat actors are individuals, groups, or organizations whose activities, capabilities, motivations, or infrastructure have been identified through intelligence and investigation.
Information about known threat actors may include:
- Preferred targets.
- Common attack techniques.
- Known infrastructure.
- Motivations.
- Operational patterns.
- Associated malware.
- Typical initial-access methods.
- Historical activity.
This information can help organizations improve threat modeling, prioritize monitoring, and develop defensive measures.
Unknown threat actors are attackers whose identity, capability, motivation, or operating methods have not been established. An organization may detect malicious activity without knowing who is responsible or whether the activity is connected to a wider campaign.
Attribution is often difficult because attackers may use compromised infrastructure, false identities, rented services, proxy systems, or techniques copied from other groups. A single observed event may therefore provide insufficient evidence to identify the responsible actor.
Security teams should avoid making unsupported attribution decisions. Defensive action should be based on observed behaviour, technical evidence, affected assets, and potential impact rather than assumptions about the attacker’s identity.
Known and Unknown Security Incidents
Known security incidents are events that have been detected, reported, investigated, or confirmed as security-related. Examples include unauthorized access, malware infection, data exposure, account compromise, service disruption, and policy violations.
When an incident is known, the organization can activate its incident response process, preserve evidence, contain the activity, remove the cause, recover affected services, and document lessons learned.
Unknown security incidents are events that have occurred but have not yet been detected or recognized. They may remain hidden because of insufficient monitoring, incomplete logs, weak alerting, lack of user reporting, or the attacker’s efforts to avoid detection.
An incident may also be partially known. For example, a security team may know that suspicious authentication activity occurred but may not know whether an account was compromised, what data was accessed, or whether the activity is still continuing.
Effective incident management should therefore distinguish between:
- What has been confirmed.
- What is suspected.
- What remains unverified.
- What evidence is missing.
- What actions are required to obtain additional information.
This distinction prevents assumptions from being treated as facts and supports more accurate incident decisions.
Known and Unknown Information
Known information is information that has been collected, validated, understood, and made available to the people who need it. In cybersecurity, this may include asset inventories, network diagrams, identity records, security policies, vulnerability reports, incident records, and threat intelligence.
Unknown information may take several forms:
- Information that has not been collected.
- Information that exists but has not been discovered.
- Information that has been collected but not analyzed.
- Information that has been misunderstood.
- Information that is outdated or incomplete.
- Information that is restricted to another team.
- Information that has not been connected to the relevant decision.
A security program should therefore focus not only on collecting more information but also on improving the quality, availability, interpretation, and sharing of information.
Centralized documentation, knowledge management, cross-functional communication, consistent reporting, and regular reviews can help convert hidden or fragmented information into recognized knowledge.
Using the Concepts for Decision-Making
Identifying What Is Known
The first step is to identify the facts that have been confirmed and understood. This may include systems, users, business processes, dependencies, security controls, vulnerabilities, incidents, and threat information.
Known information should be documented clearly and supported by reliable evidence. Where appropriate, records should include ownership, source, date, confidence level, and validation status.
Documenting What Is Not Known
Information gaps should be recorded rather than ignored. A security team may not know whether an asset is exposed, whether a vulnerability is exploitable, or whether suspicious activity represents a genuine attack.
Documenting these gaps helps assign responsibility, prioritize investigation, track progress, and prevent uncertainty from being hidden within assumptions.
Discovering Existing but Unrecognized Information
Organizations often possess information that is not available to the people making decisions. It may exist in incident reports, audit findings, technical records, individual experience, supplier documentation, or another department.
Security teams can discover this information through knowledge-sharing sessions, centralized repositories, cross-functional reviews, lessons-learned activities, and improved documentation practices.
Preparing for Unexpected Conditions
Not every event can be predicted. Organizations should therefore prepare for conditions that fall outside existing plans.
Preparation may include:
- Layered security controls.
- Tested incident response procedures.
- Backup and recovery arrangements.
- Alternative communication methods.
- Redundant services.
- Emergency decision-making processes.
- Scenario-based exercises.
- Flexible recovery plans.
The purpose is not to predict every possible event but to improve the ability to respond when assumptions fail.
Challenging Assumptions
Assumptions can create blind spots when they are treated as confirmed facts. Examples include assuming that all assets are documented, all privileged accounts are monitored, all suppliers meet security requirements, or all backups are recoverable.
Security reviews should question important assumptions and seek evidence. Independent assessments, adversarial testing, peer reviews, and lessons learned can help identify weaknesses that routine processes may overlook.
Improving Situational Awareness
Situational awareness involves understanding the environment, recognizing changes, interpreting available information, and identifying conditions that may affect decisions.
In cybersecurity, situational awareness is supported by:
- Asset visibility.
- Network and endpoint monitoring.
- Identity activity monitoring.
- Vulnerability information.
- Threat intelligence.
- Security incident reporting.
- Business context.
- Continuous risk assessment.
Good situational awareness does not require complete knowledge. It requires a reliable understanding of what is happening, what may be happening, and what remains uncertain.
Considering Alternative Scenarios
Decision-makers should consider more than one possible explanation or outcome. A suspicious event may be a false positive, a misconfiguration, an authorized activity, or an active attack.
Scenario analysis helps security teams examine different possibilities, identify warning signs, evaluate potential consequences, and prepare appropriate responses. It is particularly useful for business continuity, crisis management, critical infrastructure, and major security incidents.
Reducing Uncertainty Without Expecting Complete Certainty
The objective of cybersecurity is not to eliminate all uncertainty. Complete knowledge is rarely possible, and attempting to achieve it may delay necessary decisions.
A practical approach is to reduce avoidable uncertainty, identify the most important information gaps, improve visibility, validate assumptions, and prepare for plausible unexpected conditions.
The concepts of known and unknown encourage intellectual humility. They remind decision-makers that confidence should be based on evidence, that missing information should be acknowledged, and that unexpected conditions should be considered even when they are difficult to predict.
Conclusion
The concepts of known and unknown provide a useful way to understand knowledge, uncertainty, assumptions, and information gaps in cybersecurity. Known knowns represent established facts. Known unknowns represent recognized information gaps. Unknown knowns represent information that exists but has not been recognized or used effectively. Unknown unknowns represent conditions that have not yet been identified or considered.
Cybersecurity teams can use these concepts to improve asset visibility, threat intelligence, risk assessment, vulnerability management, incident response, security governance, and resilience. They also help organizations avoid treating incomplete information as complete knowledge.
A strong security program does not assume that everything important is already known. It continuously validates existing information, investigates recognized gaps, searches for overlooked knowledge, challenges assumptions, and prepares for unexpected events. This approach improves decision-making while recognizing that uncertainty is an enduring part of cybersecurity.
References
Online Sources
The Rumsfeld Papers – Known and Unknown: Author’s Note
Describes the meaning of the three original categories and their relationship to intelligence, strategy, and decision-making.